Does tracking a button click require consent if you collect no names, use no cookies, or only want a total? The answer depends on how the tracking works, what information it uses, its purpose, and the rules that apply to your website.
A simple event counter and a tool that connects campaigns to conversions can answer different questions and collect different data. Understanding that difference helps you choose a useful setup and connect it to your visitors’ choices.
This article explains the main EU concepts and how they relate to AutoROICalc’s JavaScript tracking module and WordPress plugins. National rules and guidance also matter; this is an introduction, not a legal assessment of an individual website.
What does website event tracking collect?
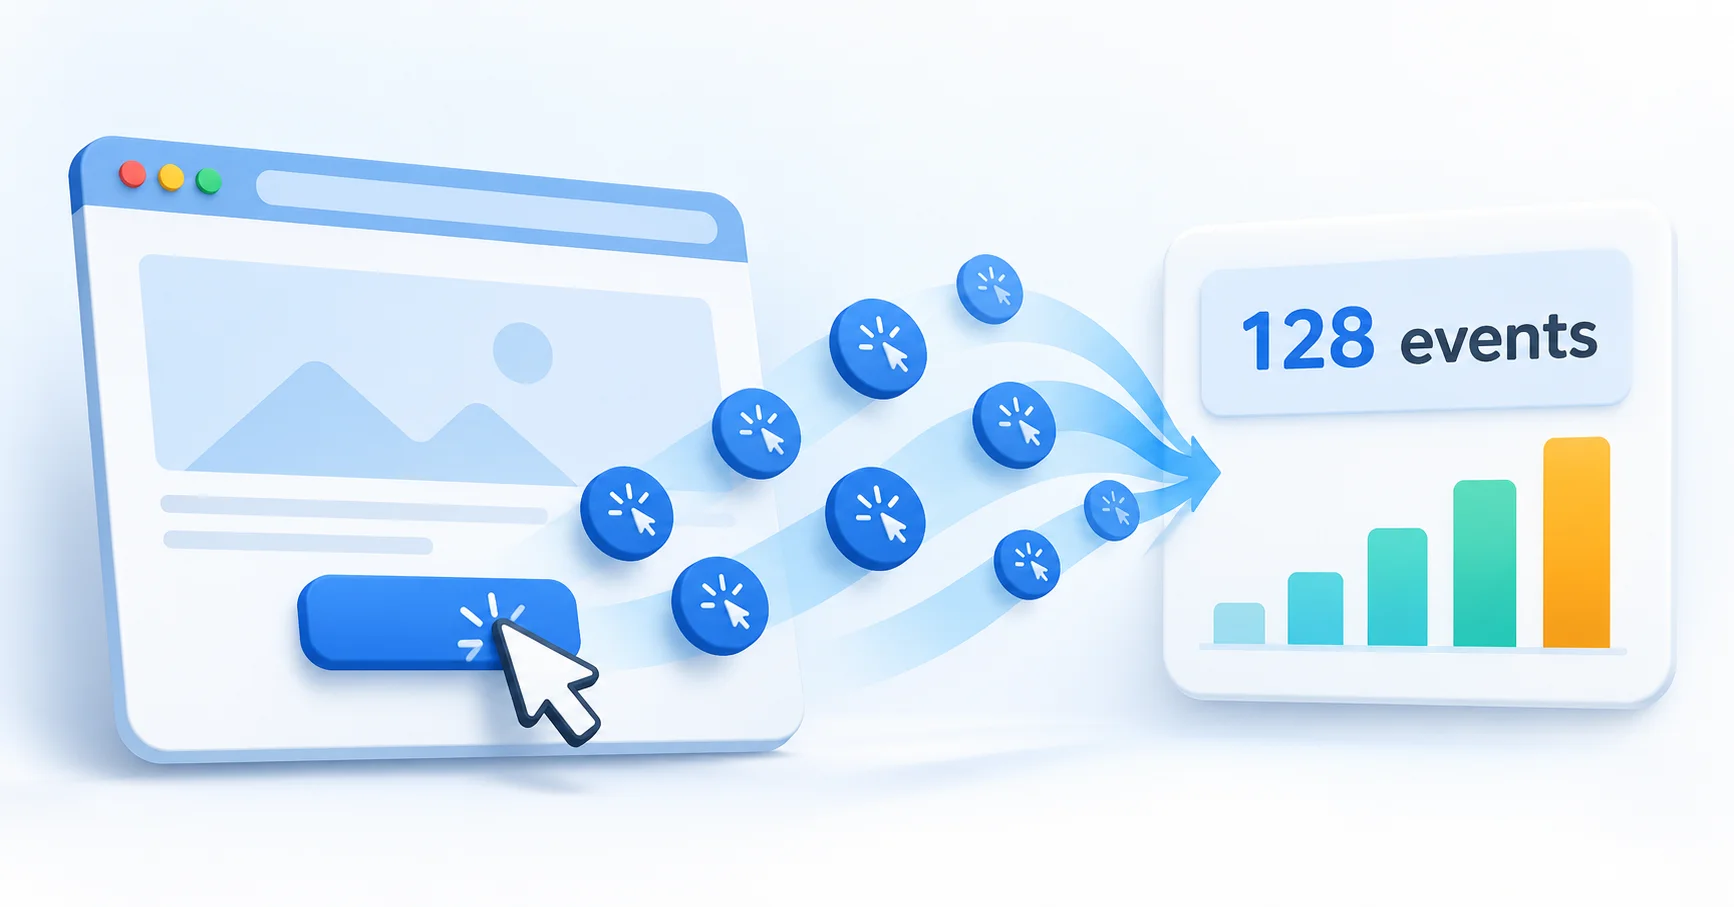
Event tracking records actions such as a button click, a hover over a product link, a form submission, or the start of checkout. The interaction itself tells you little about the data behind it.
- A counter can record that the pricing button was clicked, without linking the action to a visitor.
- Attribution tracking can attach campaign or source / medium information to an action.
- A customer journey event can include product, cart, or page context.
- A custom implementation can accidentally include personal information in labels, URLs, or submitted fields.
For example, “128 pricing-button clicks” is an event total. “Which campaign sources contributed to checkout?” requires additional context. Start with the business question, then collect only the information needed to answer it.
GDPR and ePrivacy cover different questions
Website tracking in the EU can involve both personal-data protection and rules about storing or accessing information on a visitor’s device. Calling a setup “cookie-free” addresses only part of that picture.
| Framework | Main question for website tracking |
|---|---|
| GDPR | Are you processing personal data, for which purpose, and on which lawful basis? |
| ePrivacy rules | Does the implementation store information on, or access information from, the visitor’s device, and is consent required? |
GDPR: personal data is more than names and email addresses
The European Commission’s explanation of personal data includes online identifiers such as IP addresses. Removing names does not automatically make information anonymous. Data that can still be used to identify someone, including through additional information, can remain personal data.
Genuinely anonymous information falls outside the GDPR’s personal-data rules. That assessment concerns the information and the ability to identify people, rather than the name of a tracking mode. Where personal data is processed, consent is one possible lawful basis, not the only one. See the Commission’s guidance on legal grounds for processing.
ePrivacy: the rules extend beyond cookies
Article 5(3) of the ePrivacy Directive sets a consent requirement for storing information on, or accessing information already stored on, a user’s device, with limited exceptions. These include operations needed to transmit a communication or strictly necessary to provide a service the user expressly requested. The Directive is implemented through national law.
Changing from cookies to another technique does not, by itself, settle whether the rules apply. The EDPB’s guidance on the technical scope of Article 5(3) examines techniques beyond cookies, including tracking pixels and links. It also explains that the provision can apply to information that is not personal data.
Can analytics run without consent?
Some deployments may qualify for an exception, but “analytics” is not a universal exemption. For example, the French regulator CNIL describes conditions for audience measurement without consent. These restrict the purpose to measurement for the publisher, require anonymous statistics, and exclude cross-site tracking and combining the data with other processing. Its guidance also addresses tracker lifetime and retention.
That is a national example, not a certification for every analytics tool or a rule you can automatically apply across countries. An assessment needs to cover the actual configuration, purpose, recipients, and applicable law. The word “anonymous” in a product setting does not establish that an exception applies.
Anonymous event counting versus attribution tracking
Anonymous counting is useful when an aggregate interaction total answers your question. Attribution is useful when you need campaign or source information alongside an event. Choose deliberately, because turning off a consent check does not reduce the data collected.
| Mode | What it does in AutoROICalc | Consent consideration |
|---|---|---|
| Anonymous event counting | Counts interactions through a separate path without cookies, browser storage, visitor identifiers, or captured attribution. | Reduces collected data; does not guarantee a legal exemption. |
| Consent-gated attribution | Allows attribution methods or configured events after the relevant consent signal. | Connect the visitor’s actual choices to the tracking runtime. |
| No runtime consent gate | Skips a WordPress event’s consent-category check while retaining normal event behavior. | Does not make the event anonymous or establish permission to track. |
An anonymous counter measures events rather than unique visitors. If one person clicks three times, that can produce three events. It cannot tell you how many different people clicked or which campaign each person came from.
Keep counter names static, such as “pricing_signup.” Do not put an email address, customer identifier, or personalized page value into a label. Also review infrastructure: a request still reaches a web server, and access logs may contain connection metadata. An anonymous event payload does not describe every other script or logging system on the website.
How consent works in AutoROICalc
JavaScript and npm tracking module
In version 3, the standalone module starts with Analytics and Marketing denied. Its shared attribution methods become available when either category is granted. It does not apply a separate category gate to each ordinary event, so your integration must map signals and event purposes correctly.
Your consent manager supplies the choices after the module is ready and updates them when the visitor changes their preferences. The standalone module keeps consent in memory, so provide the current choices on each page load.
Anonymous counting uses the separate sendAnonymousEvent() method. Granting consent does not add attribution to those anonymous-mode events. See the JavaScript tracking integration guide for implementation details.
WordPress Event Tracking
The Event Tracking plugin offers a separate Anonymous event counting mode for supported page elements, including click, hover, and visibility interactions.
For attribution events, keep Require explicit browser consent signal selected and choose the event’s Analytics or Marketing category. In that mode, the plugin waits for the configured category.
No runtime consent gate skips that event’s category check. The global Consent is managed by the site option bypasses internal consent checks. Both settings leave responsibility with the site’s own process; neither converts normal tracking into anonymous counting. See the WordPress Event Tracking guide.
WooCommerce journey events and checkout attribution
WooCommerce journey tracking has no anonymous event-counting mode. Its events can use Analytics, Marketing, or No runtime consent gate, and can include configured product, cart, and attribution context.
Captured checkout attribution is a separate flow. In consent-required mode, it requires Analytics consent, even when journey events use Marketing or No runtime consent gate. The site-managed consent option explicitly bypasses the internal checks.
Paid-order and refund reporting are separate server-side flows; the browser journey category does not switch them off. Server-side delivery is not, by itself, a legal exemption. Review the data and purposes separately using the WooCommerce integration guide.
A consent banner must be connected to the tracking
Displaying a banner is only one part of the setup. The tracker needs to receive the visitor’s choices and behave accordingly.
When consent is the basis, it needs to be freely given, specific, informed, and expressed through an unambiguous affirmative choice. Explain the purposes in clear language. The EU’s GDPR guidance for businesses explains these requirements.
- Pass the current consent categories after the tracking runtime is ready.
- Keep consent-gated collection waiting when no choice has been supplied.
- Update the tracker when choices change, including withdrawal.
- Check the implementation after a reload and when moving between pages.
- Test checkout attribution separately from browser journey events.
Visitors must be able to withdraw consent as easily as they gave it, as explained in the EU’s cookie guidance. AutoROICalc’s consent signal controls subsequent gated tracking; it does not automatically erase delivered records. Separately assess deletion and retention obligations when consent is withdrawn, including whether another lawful ground permits continued retention. See the Commission’s withdrawal guidance.
Why this matters for your reports
Consent choices affect what an attribution report can show. A visitor may complete an order while declining Analytics, so the order can appear without captured campaign attribution. That gap should not automatically be treated as a tracking failure.
Anonymous event totals and attributed conversions also measure different things. A counter may include repeated interactions, while attribution depends on the relevant context being available. Label reports clearly and avoid treating a click total as a unique-visitor or campaign-conversion metric.
Frequently asked questions
Do button clicks require consent if I collect no user data?
First verify what “no user data” means in the implementation. Check event fields, browser storage, identifiers, requests, and logs. Removing names alone does not answer the question; the device-access rules and the purpose also matter.
Does cookie-free tracking always avoid consent?
No. “Cookie-free” describes one technical characteristic. Other storage or access techniques may be relevant, and personal-data processing needs its own assessment.
Is No runtime consent gate the same as anonymous tracking?
No. It skips an event consent check. Normal storage, attribution, and event details may still be used. Select the separate anonymous counting mode when you want its restricted data path.
Can I keep using a site-managed consent setup?
Yes, the WordPress plugins retain their explicit site-managed options. Use them when the site’s own process controls when tracking may run. The setting itself does not obtain consent, assess an exception, or prevent collection before a visitor agrees.
Choose the smallest useful measurement setup
Begin with the question your report needs to answer. Use anonymous counters for interaction totals when appropriate, and consent-gated attribution when you need campaign context. Keep bypass settings deliberate and document which outside process controls them.
For configuration examples and a practical validation checklist, read Tracking and Consent in AutoROICalc.